Security safeguards for the Digital Personal Data Protection Act
The DPDP Act requires every data fiduciary to protect personal data with reasonable security safeguards and to report personal data breaches. Ciyora helps you control who can reach personal data, notice when something goes wrong, and show what you did about it.
What the Act asks of a data fiduciary
The Digital Personal Data Protection Act, 2023 applies to the processing of digital personal data in India. Among other duties, a data fiduciary must take reasonable security safeguards to prevent personal data breaches, notify the Data Protection Board of India and each affected data principal of a breach, erase personal data when it is no longer needed for its purpose, and give data principals a way to have grievances addressed. The DPDP Rules made under the Act add detail on these obligations.
Ciyora is a security platform, not a consent manager or a privacy-request portal. It helps with the security safeguards, breach readiness and accountability parts of the Act, including for the personal data your own security tools process about employees.
Hosting location
Ciyora is hosted in India and data stays in India. Your sector rules and contracts can include expectations about where data is stored and processed, so confirm the hosting arrangements meet your obligations before you adopt the hosted service.
How Ciyora maps to the requirement areas
Each row names a control area, what Ciyora does for it, and the evidence it can produce. Your own policies, people and processes still matter: the platform helps you operate and evidence the controls.
| Requirement area | How Ciyora helps | Evidence you can produce | Modules |
|---|---|---|---|
| Reasonable security safeguards: access control | Least-privilege access to systems that hold personal data, with requests, approvals, reviews, just-in-time privilege and recorded privileged sessions. | Access reviews, privileged access reports and session recordings for systems holding personal data. | Fortress |
| Reasonable security safeguards: network and configuration | Zero-trust network access to data stores; cloud posture checks for public exposure, encryption and logging settings. | Access policy history; posture findings such as publicly readable storage and their remediation. | VPN, Armor |
| Detecting a personal data breach | Detections for credential theft, unusual access and data exfiltration patterns; endpoint data-protection events for file transfers, USB and AI tools. | Alerts and incidents with the affected identities, assets and data noted. | Detect, Monitor |
| Breach response and notification | Incident timelines that record when a breach was detected, who handled it and what was done, to support notifications to the Board and data principals. | Incident timelines and response records. | Detect |
| Retention and erasure | Retention periods per data type in Ciyora settings, including monitoring data such as screenshots, so security data about people is not kept longer than needed. | Retention settings and their change history. | Comply, Monitor |
| Knowing where personal data lives | Inventory of assets, SaaS applications and cloud resources, with sensitivity and who has access. | Asset and SaaS inventories with access lists. | Discover, Fortress |
| Accountability | Hash-chained audit log of administrative actions, approvals and data access decisions. | Audit exports and chain verification. | Comply |
Your security tools process personal data too
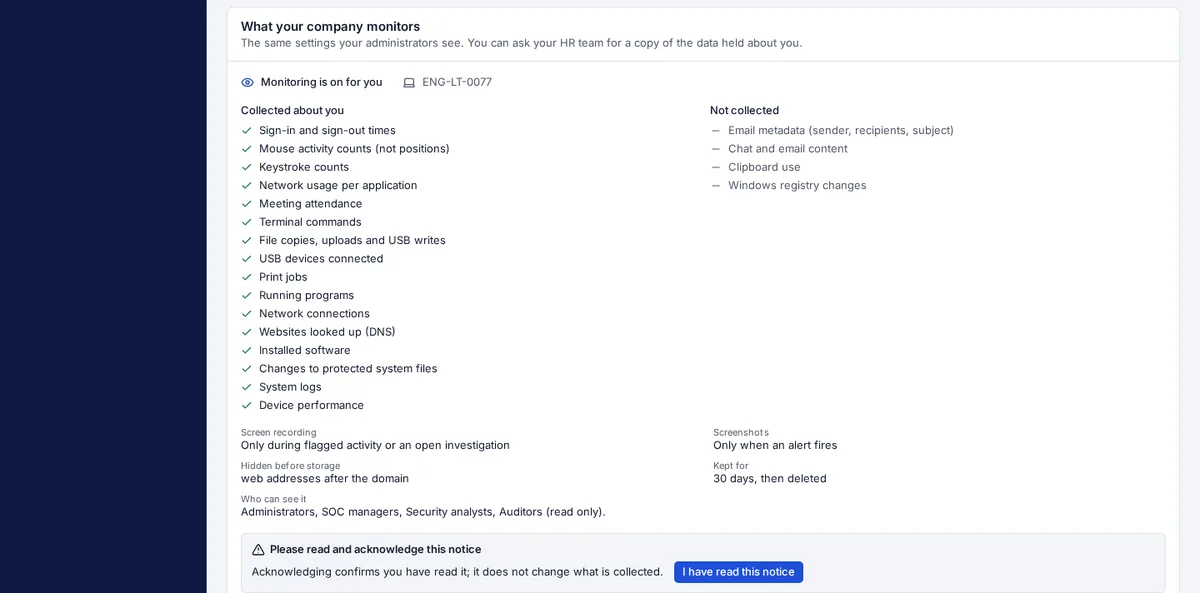
Endpoint monitoring and identity governance involve personal data about employees and contractors. Ciyora Monitor is built for transparent monitoring: employee notices, acknowledgements and audit trails are built in, and each employee can see what is collected about them. Organisations configure monitoring under their own legal obligations; the lawful basis and the policy remain your decisions. How Ciyora Monitor handles privacy.
Please note. Ciyora is not a certification and does not make an organization compliant on its own. This page describes how Ciyora capabilities map to requirement areas and help you produce evidence. Always read the current text of the regulation or standard and take advice from your compliance team, auditors or legal counsel.
Walk through your control set with us
Bring your latest audit observations or gap assessment, and we will show where Ciyora fits and where it does not.