Security controls and evidence for RBI regulated entities
Banks, NBFCs and other RBI regulated entities are expected to govern who can access critical systems, watch for attacks around the clock, respond and report quickly, and prove all of it to auditors. Ciyora Fabric brings those controls into one platform.
The regulatory picture
The Reserve Bank of India sets cyber security and IT governance expectations through several instruments, including the Cyber Security Framework in Banks (2016) and the Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices (2023), which applies to banks and to many NBFCs and other regulated entities. Incident reporting also has to fit CERT-In's directions for reporting cyber incidents.
Common themes across these instruments are strong control of privileged and user access, continuous logging and monitoring, timely vulnerability and patch management, secure configuration, incident response and reporting, and audit trails that examiners can rely on. That is the ground Ciyora covers.
Hosting location
Ciyora is hosted in India and data stays in India. RBI directions can include expectations about where data is stored and processed, so confirm the hosting arrangements meet your obligations before you adopt the hosted service.
How Ciyora maps to the requirement areas
Each row names a control area, what Ciyora does for it, and the evidence it can produce. Your own policies, people and processes still matter: the platform helps you operate and evidence the controls.
| Requirement area | How Ciyora helps | Evidence you can produce | Modules |
|---|---|---|---|
| User access management | Joiner, mover and leaver automation from the HR source; access requests with approval; periodic access reviews with reasons required for high-risk decisions. | Access review evidence packs with every decision, reviewer, time and comment; joiner-mover-leaver activity reports. | Fortress, Comply |
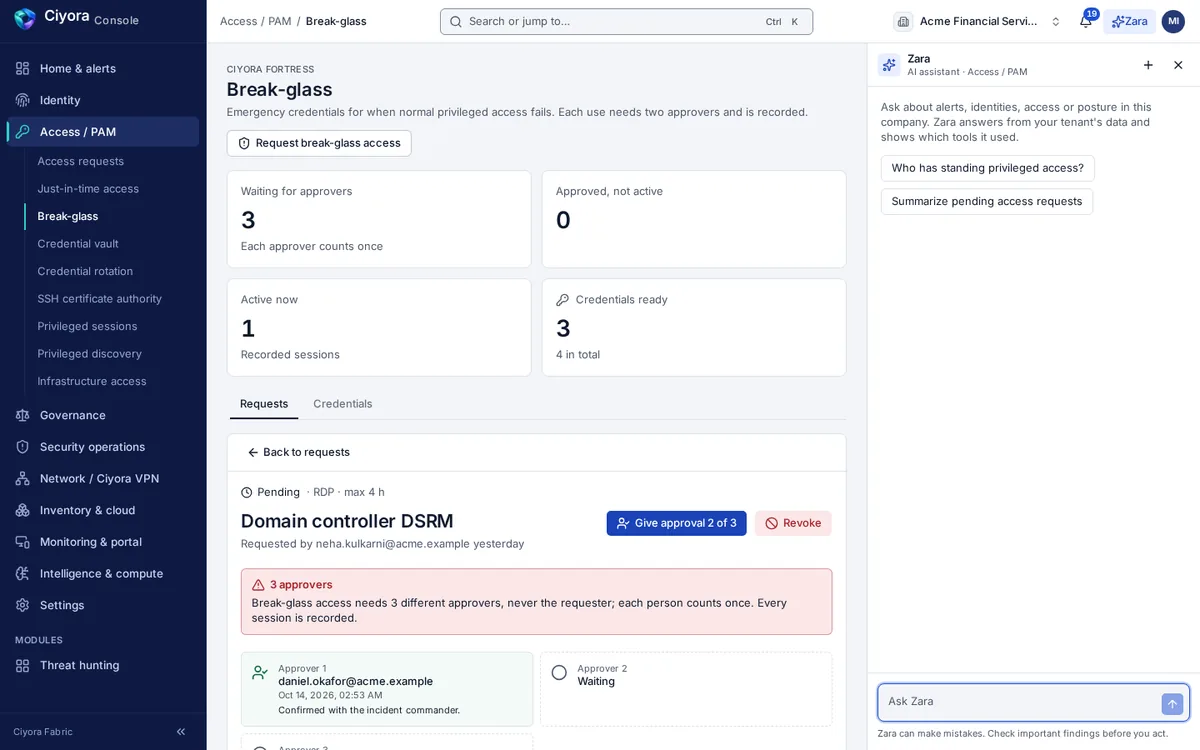
| Privileged access | Credential vault with check-out, rotation and security-key step-up; just-in-time elevation; break-glass with multiple approvers; recorded SSH, RDP and VNC sessions. | Privileged access reports, vault check-out logs, rotation history and session recordings. | Fortress |
| Segregation of duties | Preventive SoD checks on access requests, detective scans across applications, and recorded exceptions. | SoD violation and exception reports. | Fortress, Comply |
| Logging and security monitoring | Central log collection, Sigma-based detections mapped to MITRE ATT&CK, XDR correlation into incidents and threat intelligence matching. | Detection coverage by ATT&CK technique, alert and incident history, log search. | Detect |
| Incident response and reporting | Incident queue with owner, status and timeline; response actions and playbooks run with confirmation; timestamps for detection and each action. | Incident timelines that support your internal and regulatory reports. | Detect |
| Vulnerability and patch management | Asset inventory with software versions; vulnerabilities ranked by CVSS, EPSS and the CISA KEV list; external attack surface discovery. | Vulnerability status by asset and severity over time. | Discover |
| Secure configuration and cloud | Cloud posture checks against CIS benchmarks; findings with remediation and workflow; excessive cloud permissions. | Posture score history and control pass rates per framework. | Armor |
| Network access and segmentation | Zero-trust access by identity, group and device tag; deny by default; device posture; no inbound ports for remote access. | Versioned access policy with history, device and route inventory. | VPN |
| Data leak prevention | Endpoint events for file transfers, USB devices and data sent to AI tools, with policies, with employee notices built in. | Data-protection event and violation history. | Monitor |
| Audit trail integrity | Hash-chained audit log, verifiable in the browser and on the server. | Audit exports and chain verification results. | Comply |
Please note. Ciyora is not a certification and does not make an organization compliant on its own. This page describes how Ciyora capabilities map to requirement areas and help you produce evidence. Always read the current text of the regulation or standard and take advice from your compliance team, auditors or legal counsel.
Walk through your control set with us
Bring your latest audit observations or gap assessment, and we will show where Ciyora fits and where it does not.