One platform for identity, access, detection and posture
Ciyora Fabric brings identity governance, privileged access, zero-trust networking, detection and response, cloud posture and compliance into one console, on one tenant and one audit trail. Built for regulated organizations in India.
Hosted in India · data stays in India. Data processing follows DPDP Act 2023 obligations. Gateways dial out, so there are no inbound ports to open.
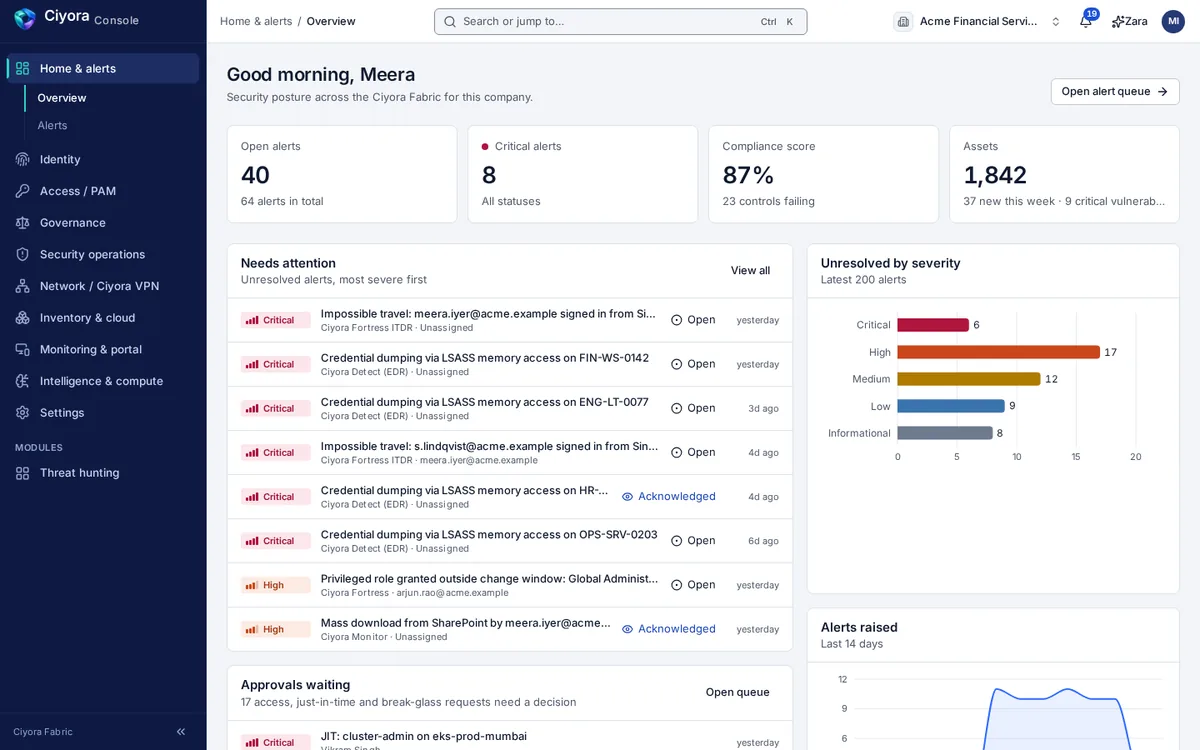
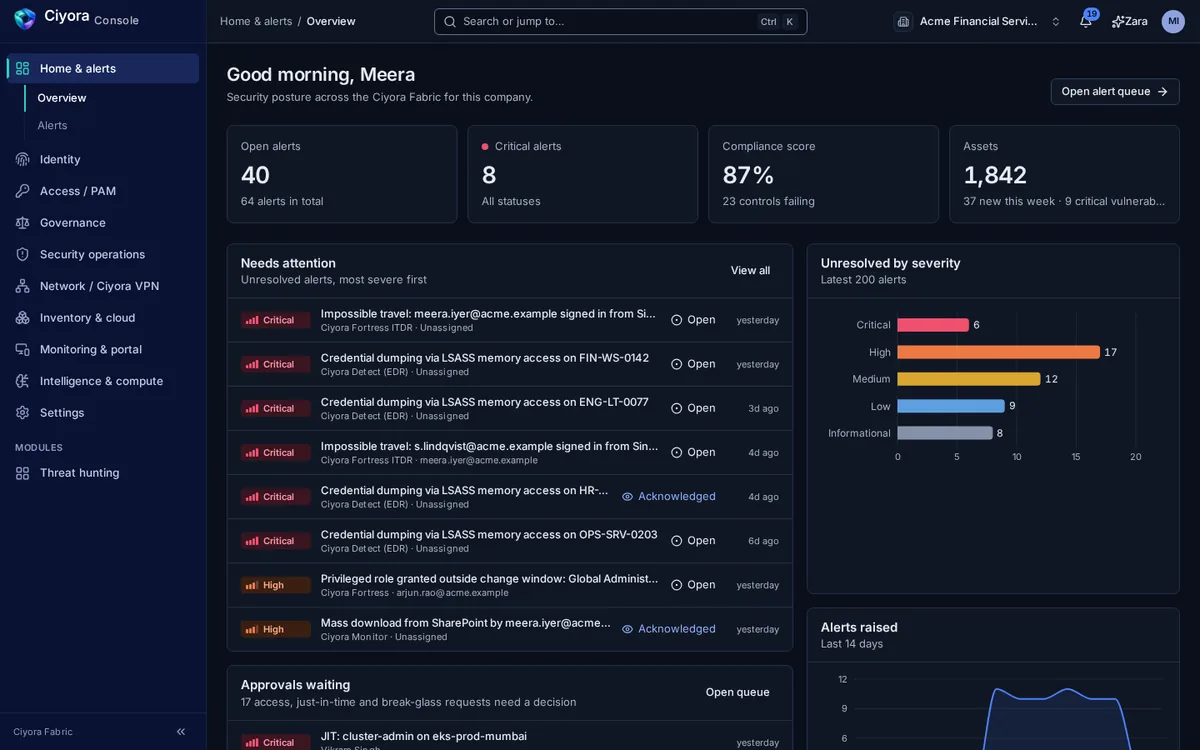
Nine modules, one fabric
Start with the module you need most. Each one shares the same identities, assets, alerts and audit chain, so adding the next one does not mean another integration project.
Identity and access
Who has access, why, for how long, and over which network path.
Detection and response
Telemetry from endpoints, identities, networks and logs, correlated into incidents.
Exposure and posture
What you own, how it is configured, and how that maps to your controls.
Ciyora Discover
Asset inventory, network scans, software and vulnerability exposure, prioritised by CVSS, EPSS and CISA KEV.
Explore Ciyora DiscoverCiyora Armor
Cloud security posture and cloud entitlements (CIEM) across AWS, Azure and Google Cloud.
Explore Ciyora ArmorCiyora Comply
Controls, evidence and reports that tie platform activity to the frameworks your auditors use.
Explore Ciyora ComplyIntelligence
AI that works inside the platform, on your tenant data, under your rules.
Designed to sit safely inside regulated networks
The design choices that matter to a security review are made once, in the platform, and every module inherits them. How Ciyora Fabric is built.
Gateways dial out
Site gateways, collectors and clients open outbound connections to Ciyora Fabric. You do not open inbound ports.
Tenant isolation
Every request is scoped to one tenant, chosen from the signed-in organization and checked on every API call.
Hash-chained audit
Each audit entry carries the hash of the one before it, so a changed or deleted entry breaks the chain.
Hosting
Hosted in India · data stays in India. Data processing follows DPDP Act 2023 obligations.
Built in Go
Services, gateways and the endpoint client are Go binaries: small, fast to start and simple to operate.
One console for every team that touches security
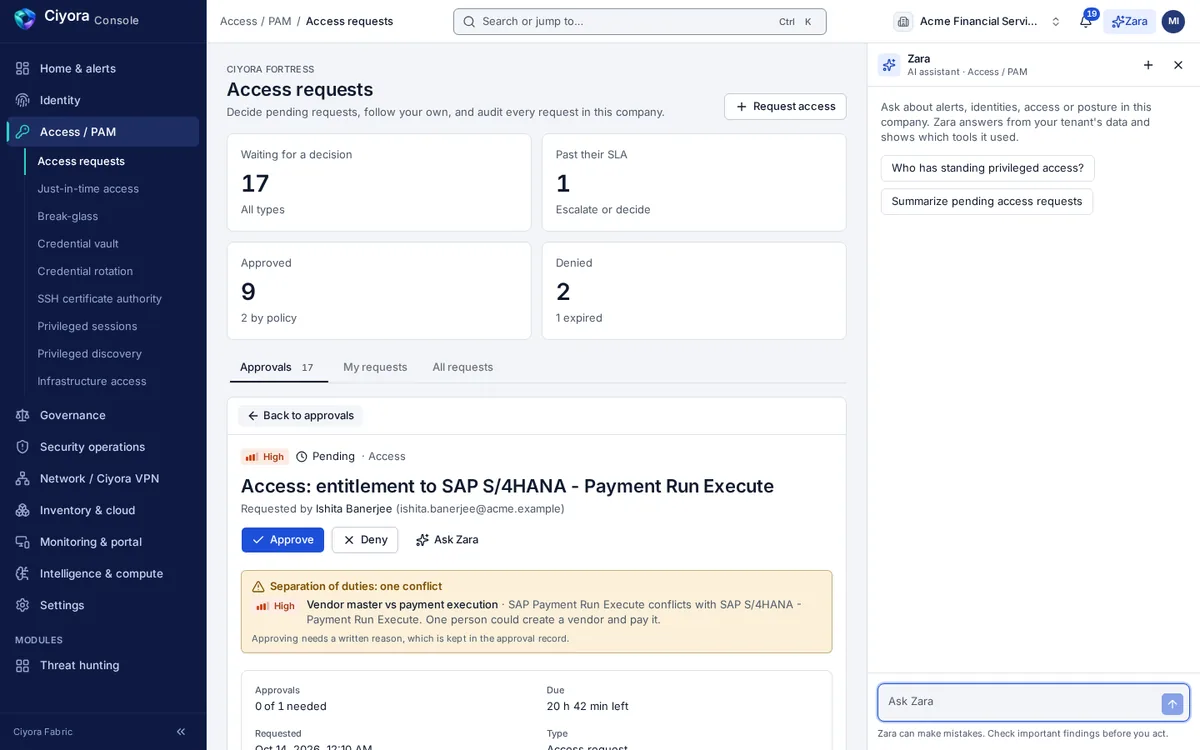
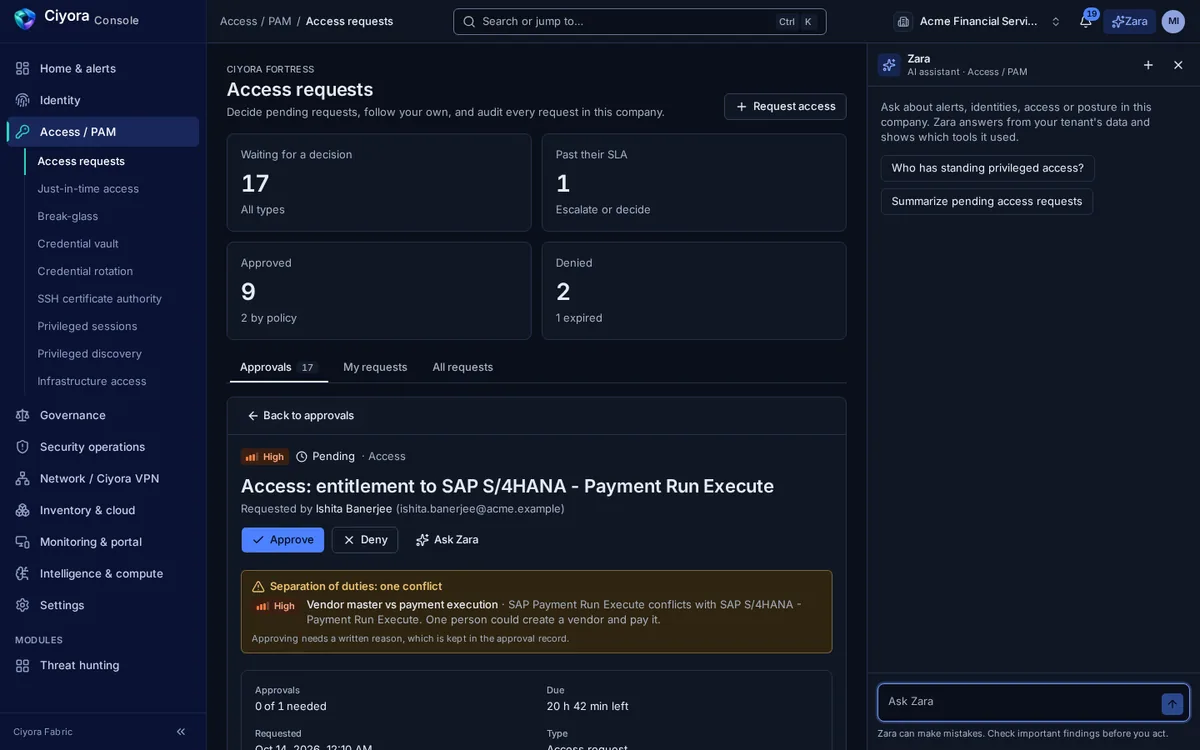
Administrators, SOC analysts, auditors, approvers and employees each see the part of the platform their role allows. Approvals carry their separation-of-duties check with them, and every decision asks for a reason that lands in the audit trail.
- Role-aware navigation across identity, access, governance, security operations, network, inventory and monitoring
- Search and jump to any page or identity with Ctrl+K
- Light and dark themes, keyboard navigation and layouts that work on a phone
A single client on every laptop and server
Ciyora Client runs as a system service on Windows, macOS and Linux. It joins the device to the Ciyora VPN mesh, resolves internal names through split DNS and reports device posture, with a tray app for people and a command line for servers.
- WireGuard tunnels with NAT traversal and relay fallback
- Optional kill switch and subnet router mode
- Connection profiles per tenant, deliverable through MDM
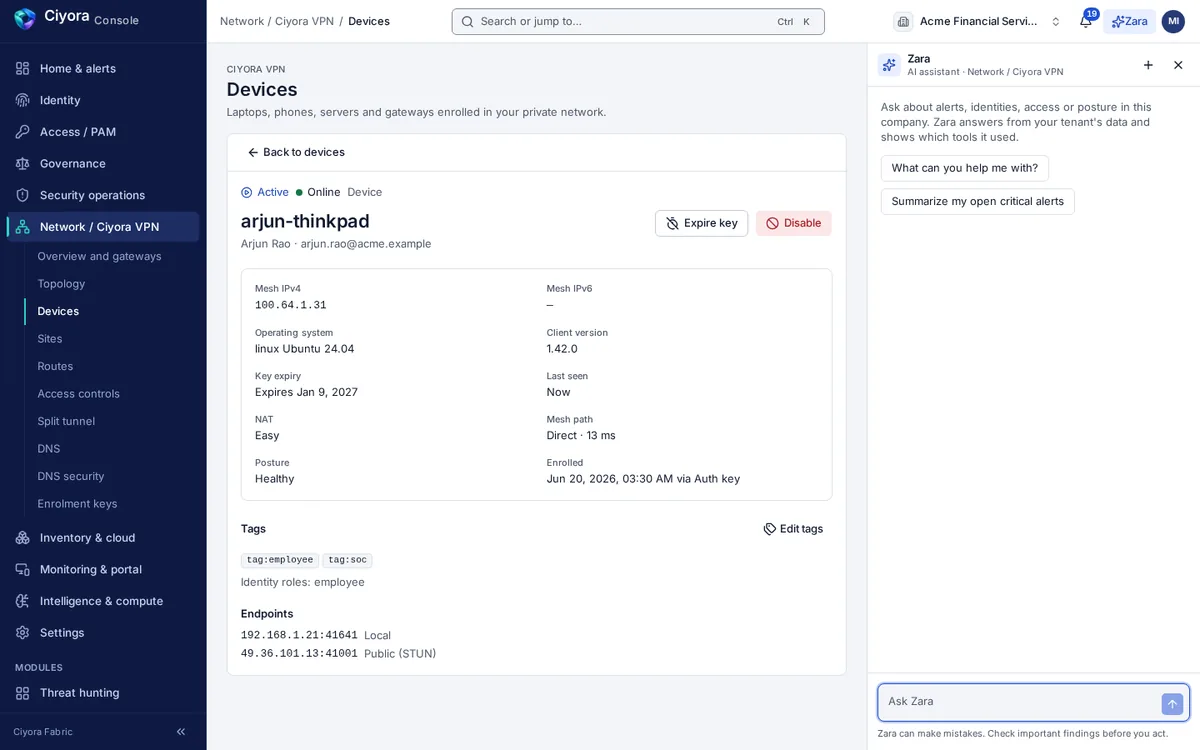
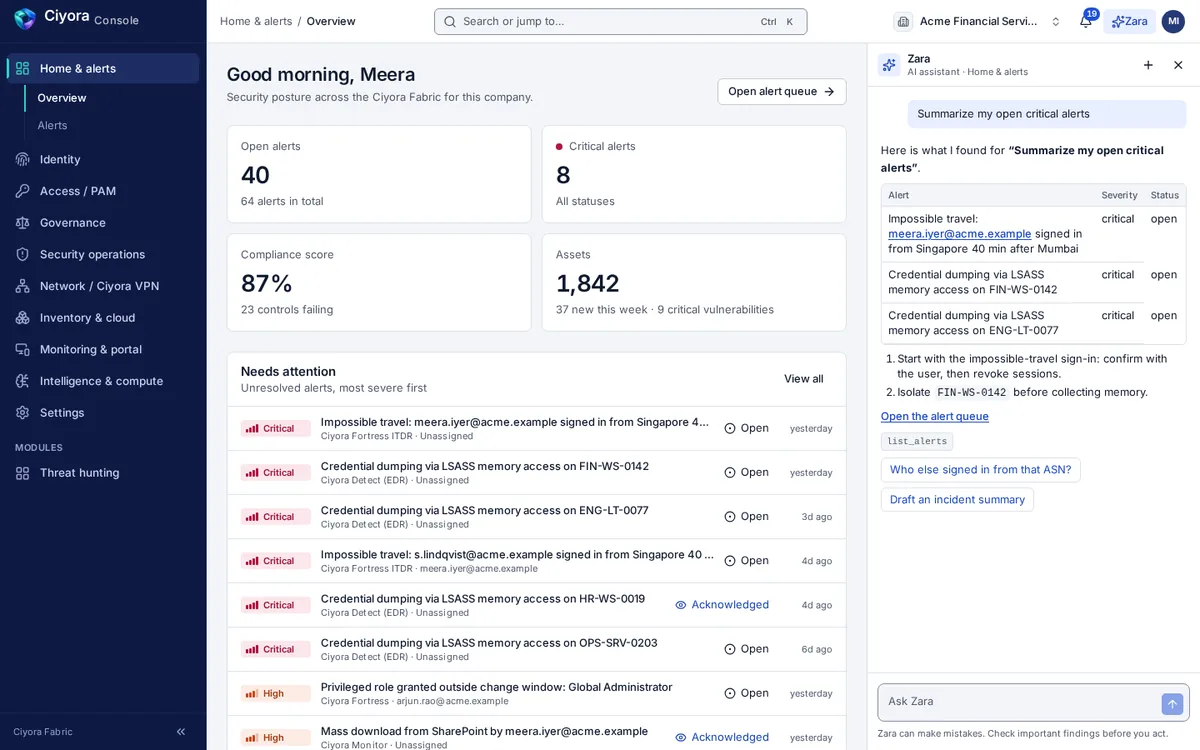
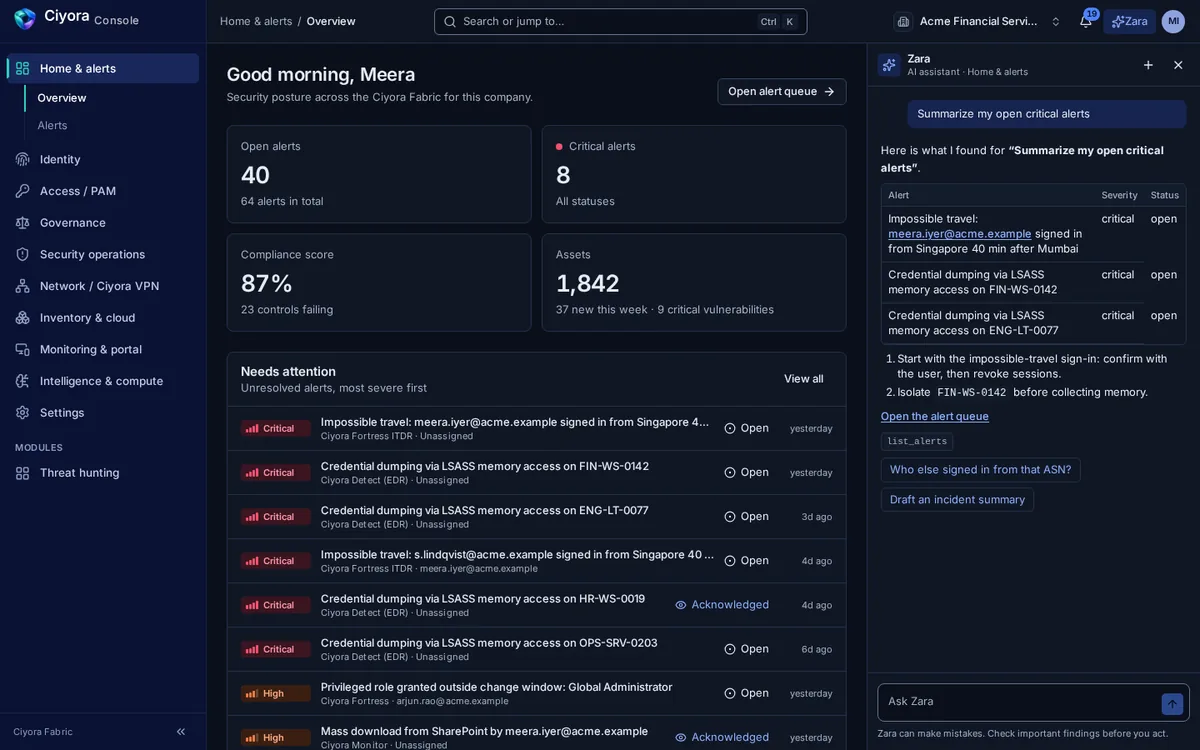
An assistant that shows its work
Zara sits beside every page of Ciyora Console. Ask about alerts, identities, access or posture and it answers from your tenant's data, names the tools it used and suggests the next step. You decide what happens next.
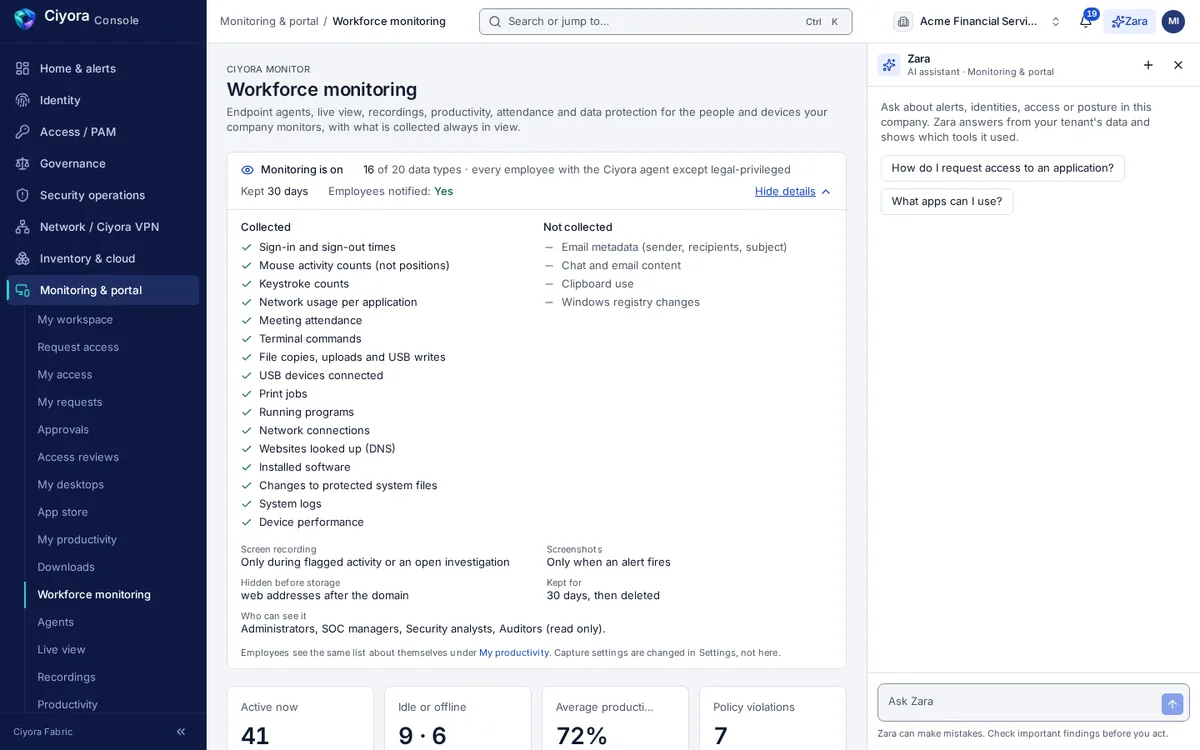
Built for transparent monitoring
Employee notices, acknowledgements and audit trails are built in. Operator screens state what is collected, from whom and for how long, and organisations configure monitoring under their own legal obligations.
Built for regulated industries in India
Ciyora does not make you compliant on its own. It gives you the controls and the evidence that RBI, SEBI, DPDP and ISO 27001 programmes ask for, in one place.
Banks and NBFCs (RBI)
Privileged access, access reviews, monitoring and audit evidence for RBI cyber security expectations.
Read moreSEBI regulated entities
How Ciyora capabilities map to the identify, protect, detect, respond and recover goals of SEBI CSCRF.
Read moreDPDP Act 2023
Access control, transparent monitoring and breach detection that support your data fiduciary duties.
Read moreISO/IEC 27001:2022
Evidence for access control, logging, monitoring, vulnerability and incident controls in your ISMS.
Read moreSee Ciyora Fabric on a sample tenant
A walkthrough of the modules you care about, followed by a technical session with your security architects.